We value thought-leadership at Fortuna Cysec
Threat Intelligence & Vulnerability Management
Just two days after emergency security updates addressed the critical PHP2Shell vulnerabilities, the PHP development team disclosed another potential remote code execution (RCE) vulnerability, CVE-2026-115560, affecting PHP's session upload progress functionality.
Unlike the earlier PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619), this newly identified issue remains unpatched as of October 23, 2026 and affects applications using a specific, uncommon combination of PHP session configurations.
Although PHP considers exploitation unlikely in typical deployments, successful exploitation under the required conditions could potentially allow attackers to execute malicious code remotely.
Organizations should review their PHP configurations and implement the recommended mitigation until an official security update becomes available.
Understanding CVE-2026-115560
CVE-2026-115560 involves PHP's session upload progress functionality, which tracks file upload progress using session data.
The vulnerability becomes exploitable only when several specific conditions exist simultaneously:
- The application configures
session.serialize_handlerasphp_binaryorphp_serialize. - Application code changes the serialization handler to
phpat runtime usingini_set(). - This change occurs before calling
session_start(). - PHP session upload progress remains enabled.
Under these conditions, improper session-state handling may create a potential remote code execution path.
Applications that do not dynamically change their session serialization handler are not exposed to this specific attack vector.
Why This Vulnerability Matters
Although exploitation requires an uncommon configuration, organizations should not overlook the potential security impact.
Successful exploitation could result in:
- Remote code execution: Unauthorized execution of commands within the PHP server process.
- Application compromise: Attackers gaining control over affected web applications.
- Data exposure: Unauthorized access to sensitive application information.
- Business disruption: Potential interruption of websites and critical business services.
- Lateral movement: Attackers using a compromised web server to target connected infrastructure.
Importantly, the emergency PHP releases issued on October 21, 2026, do not address CVE-2026-115560.
Organizations that have already patched PHP2Shell should still verify whether their applications use the vulnerable configuration.
Affected PHP Versions and Patch Status
As of October 23, 2026, PHP has not published a definitive affected-version list or a confirmed fixed-release number for CVE-2026-115560.
Security DetailCurrent StatusCVE IdentifierCVE-2026-115560Vulnerability TypePotential Remote Code ExecutionAffected ComponentPHP Session Upload ProgressCVSS ScoreNot officially publishedSecurity PatchNot yet availableRecommended FixDisable session upload progressPermanent ResolutionExpected in next regular PHP release
PHP plans to address this vulnerability in its next regular maintenance release rather than issuing another emergency update.
Recommended Mitigation and Security Measures
Fortuna Cysec recommends the following actions.
1. Disable PHP Session Upload Progress
Until an official patch is released, disable the affected feature in the PHP configuration:
session.upload_progress.enabled = 0
Apply the setting in php.ini or an appropriate server-level configuration and restart affected PHP services or workers.
2. Review Application Session Configurations
Identify applications using php_binary or php_serialize session handlers and determine whether application code changes the handler dynamically before starting sessions.
3. Maintain Existing PHP2Shell Patches
Ensure PHP installations remain updated to the security releases addressing CVE-2026-109618 and CVE-2026-109619.
These updates remain essential even though they do not resolve CVE-2026-115560.
4. Strengthen Security Monitoring
Monitor PHP application logs, unusual session activity, unexpected server processes, and suspicious HTTP requests. Maintain updated WAF protections where available.
5. Track the Official Security Update
Monitor PHP security advisories and deploy the permanent fix once the next regular release becomes available.
Organizations that already disabled session upload progress as part of their PHP2Shell mitigation do not need an additional configuration change for this vulnerability.
How Fortuna Cysec Can Help
CVE-2026-115560 demonstrates that applying security patches alone may not eliminate every emerging threat. Continuous visibility, configuration assessment, and proactive monitoring remain essential.
Through the Fortunox Security Operations Platform, Fortuna Cysec combines Continuous Threat Exposure Management (CTEM) and Managed Detection and Response (MDR) to help organizations:
- Identify vulnerabilities: Discover exposed assets, vulnerable configurations, and emerging security risks.
- Prioritize remediation: Assess business impact and coordinate risk-based corrective actions.
- Monitor threats: Detect suspicious activity through 24/7 managed security operations.
- Respond effectively: Investigate incidents and coordinate containment and remediation.
- Maintain resilience: Continuously monitor and improve organizational security posture.
Our integrated security approach helps organizations move beyond reactive patching toward continuous threat exposure reduction.
Final Thoughts: Mitigate Now, Patch When Available
While CVE-2026-115560 requires an uncommon application configuration, its potential remote code execution impact warrants attention.
Organizations should review PHP session configurations, disable session upload progress where appropriate, maintain existing PHP security updates, and monitor for the permanent fix.
Emerging vulnerabilities demand continuous visibility, proactive remediation, and rapid threat detection.
Is Your PHP Environment Secure?
Fortuna Cysec helps organizations identify critical vulnerabilities, assess security exposure, and strengthen cyber resilience through Fortunox CTEM and MDR services.
Contact Fortuna Cysec today to assess your cybersecurity exposure and strengthen your defenses.
CVE-2026-115560: New PHP Remote Code Execution Vulnerability Remains Unpatched
Critical Cybersecurity Advisory
Threat Intelligence & Vulnerability Management
Two critical PHP vulnerabilities, collectively known as PHP2Shell, have raised significant security concerns for organizations running PHP-based websites and applications. Tracked as CVE-2026-109618 and CVE-2026-109619, these vulnerabilities carry a critical CVSS score of 9.2 and could allow unauthenticated attackers to execute malicious code remotely on vulnerable servers. Unlike vulnerabilities affecting individual plugins or applications, PHP2Shell impacts the underlying PHP runtime, potentially exposing platforms such as WordPress, Drupal, Joomla, Magento, and custom PHP applications. With exploitation attempts already reported, organizations should prioritize immediate patching and security monitoring.
Understanding the PHP2Shell Vulnerabilities
CVE-2026-109618: Out-of-Memory Memory Corruption
This vulnerability involves improper memory handling when PHP encounters certain out-of-memory conditions. Attackers may exploit specially crafted HTTP requests to trigger memory corruption and potentially achieve remote code execution.
Potential impact:
- Unauthorized server access and code execution
- Web application compromise
- Data theft and service disruption
CVE-2026-109619: Use-After-Free Vulnerability
This vulnerability occurs when PHP improperly retains references to previously released memory during request processing. Attackers may manipulate these conditions to execute arbitrary code within affected PHP processes.
Potential impact:
- Remote code execution
- Exposure of sensitive application data
- Compromise of application sessions and credentials
- Potential lateral movement within connected environments
Both vulnerabilities demonstrate how weaknesses in core application infrastructure can create significant enterprise-wide security exposure.
Affected PHP Versions and Security Fixes
PHP released emergency security updates on October 21, 2026.
PHP VersionFixed ReleaseActionPHP 8.58.5.12Update immediatelyPHP 8.48.4.27Update immediatelyPHP 8.38.3.36Update immediatelyPHP 8.28.2.35Update immediatelyPHP 8.1 and olderEnd of life upstreamMigrate or apply verified vendor security backports
Organizations should validate the PHP versions running across web servers, cloud workloads, containers, and hosted applications.
Important: Updating a CMS or its plugins alone does not remediate PHP2Shell. The underlying PHP runtime must be patched. Vendor-maintained distributions may provide security backports without changing the upstream version number.
Why Organizations Should Act Immediately
PHP powers a significant portion of the internet, making these vulnerabilities a potentially widespread threat.
Security researchers have reported exploitation attempts, including activity observed before public disclosure.
Successful exploitation could result in:
- Data breaches: Unauthorized access to sensitive customer and business information
- Business disruption: Compromise or downtime of critical websites and applications
- Infrastructure compromise: Attackers gaining a foothold for further network intrusion
- Compliance exposure: Potential regulatory and contractual consequences
Organizations running internet-facing PHP applications face particular urgency.
Recommended Remediation and Security Measures
Fortuna Cysec recommends the following immediate actions:
1. Identify vulnerable assets
Inventory PHP installations across websites, applications, servers, cloud environments, and containers. Prioritize internet-facing systems.
2. Apply security patches
Upgrade to the appropriate fixed PHP release or verified vendor-patched package. Rebuild affected container images and restart PHP workers to ensure updated code is running.
3. Implement temporary mitigations
Where immediate patching is not possible:
- Restrict HTTP request and upload sizes.
- Evaluate
memory_limit=-1for CVE-2026-109618, considering resource-exhaustion risks. - Disable
session.upload_progress.enabledfor CVE-2026-109619. - Disable
fatal_error_backtraceson affected PHP 8.5 deployments. - Strengthen WAF protections and request filtering.
These mitigations reduce specific exploitation paths but do not replace security patching.
4. Monitor for exploitation
Investigate unusual PHP worker crashes, suspicious HTTP requests, unexpected processes, unauthorized file changes, and abnormal outbound connections.
5. Validate remediation
Confirm patched versions are deployed, affected services have restarted, and security monitoring remains operational. Investigate any evidence of possible compromise.
How Fortuna Cysec Helps Protect Your Organization
PHP2Shell highlights the importance of continuous vulnerability visibility, proactive risk management, and rapid threat detection.
Through the Fortunox Security Operations Platform, Fortuna Cysec combines Continuous Threat Exposure Management (CTEM) and Managed Detection and Response (MDR) to help organizations:
- Identify exposures: Discover vulnerable assets and prioritize critical security risks.
- Accelerate remediation: Track vulnerabilities and coordinate risk-based remediation.
- Detect threats: Monitor suspicious activity through 24/7 managed security operations.
- Respond effectively: Investigate security incidents and coordinate containment and recovery.
- Strengthen resilience: Maintain continuous visibility into evolving threats and security posture.
Our integrated approach helps organizations move beyond reactive vulnerability management toward continuous security risk reduction.
Final Thoughts: Patch Today, Protect Continuously
PHP2Shell is a reminder that even mature, widely adopted technologies can introduce critical security risks.
Organizations should immediately identify affected PHP installations, deploy security updates, implement appropriate protective controls, and monitor for potential exploitation.
Cybersecurity is not just about identifying vulnerabilities. It is about reducing exposure before attackers exploit it.
Is Your Organization Exposed to PHP2Shell?
Fortuna Cysec can help assess your exposure, prioritize remediation, and strengthen your defenses through Fortunox CTEM and MDR services.
Contact Fortuna Cysec today to strengthen your organization's cybersecurity posture.
PHP2Shell: Critical PHP Vulnerabilities Expose Web Applications to Remote Code Execution
Critical Cybersecurity Advisory
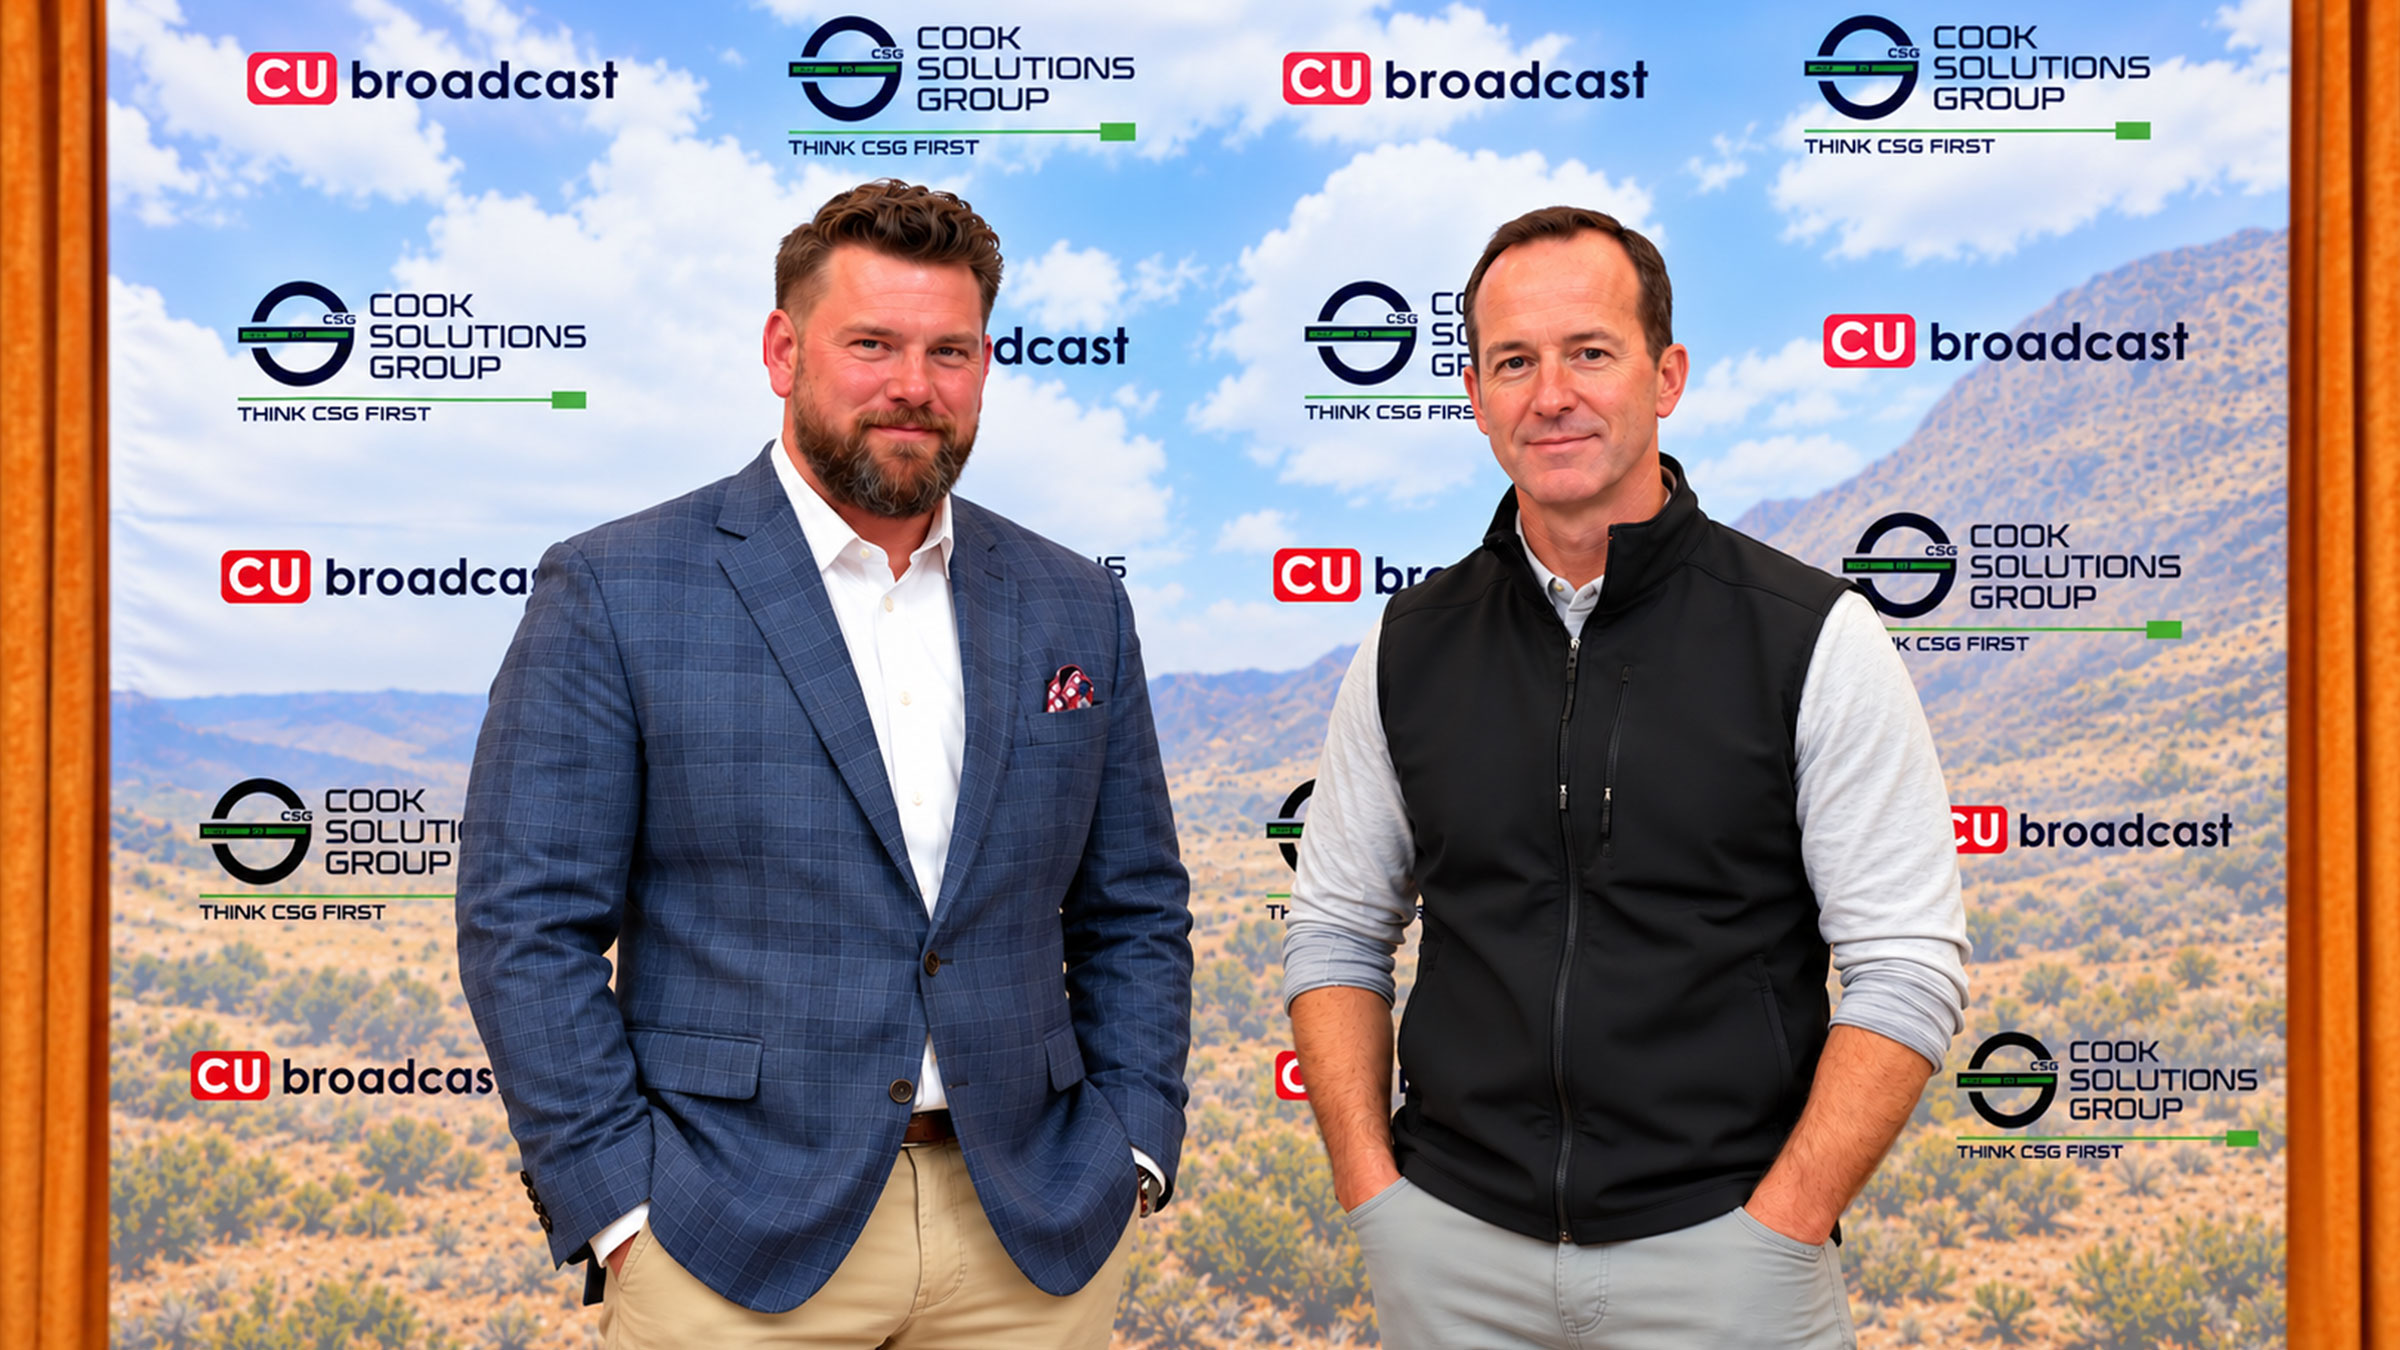
At the 2026 America's Credit Unions Operations & Technology Council Conference in Las Vegas, Fortuna Cysec's VP of Sales, Patrick Whelan, joined Mike Lawson of CUbroadcast to discuss the evolving cybersecurity challenges facing credit unions and financial institutions.
The conversation explores why traditional, reactive cybersecurity strategies are no longer sufficient as threats evolve beyond ransomware to include data theft, extortion, and AI-driven risks.
Key topics include:
- Proactive Cybersecurity: Shifting from responding to incidents to identifying and eliminating risks before they can be exploited.
- Risk-Based Vulnerability Management: Prioritizing remediation using asset criticality, sensitive data exposure, and exploitability rather than vulnerability scores alone.
- Identity Security and AI: Addressing the emerging risks of non-human identities, AI agents, and increasingly complex access management.
- Operational Maturity: Reducing repetitive security incidents through root cause analysis, remediation, and continuous improvement.
- Board-Level Security Strategy: Building the business case for proactive cybersecurity investments while balancing risk, operational efficiency, and budget constraints.
Discover how Fortuna Cysec helps organizations maximize their existing security investments, accelerate remediation, and build a more proactive, resilient cybersecurity posture.
About Fortuna Cysec
Fortuna Cysec is a global cybersecurity company offering Fortunox - an integrated AI-native Security Operations Platform that centralizes AI-powered threat detection, automated response, compliance management and true 24x7 managed detection and response. By combining advanced analytics, automated actions and expert-led response in one integrated system, Fortuna Cysec gives organizations a faster, smarter and more resilient way to defend their environments. For more information, visit www.fortunacysec.com.
Credit Union Cybersecurity: Moving from Reactive Defense to Proactive Risk Reduction
At the 2026 America's Credit Unions Operations & Technology Council Conference in Las Vegas, Fortuna Cysec's VP of Sales, Patrick Whelan, joined Mike Lawson of CUbroadcast to discuss the evolving cybersecurity challenges facing credit unions and financial institutions.
ATLANTA, Oct 22, 2026 -- Fortuna Cysec, a global cybersecurity company offering integrated AI-native security operations managed detection and response, continuous threat exposure management and compliance services, today announced it has been selected to provide Third-Party Risk Management services for a leading global health technology company focused on improving patient outcomes through connected care solutions delivered in the home.
The engagement will support vendor onboarding, evidence collection, assessment execution, risk reporting and ongoing platform management across the organization's third-party ecosystem.
Through the partnership, Fortuna Cysec will leverage the partner’s existing environment to streamline third-party risk workflows, drive greater consistency in assessments, and enhance visibility into vendor risk posture. Fortuna Cysec will support approximately 500 third-party risk assessments annually, alongside delivering operational reporting, SLA tracking and governance reviews designed to strengthen transparency and accountability.
The scope of services Fortuna Cysec provides includes rapid vendor engagement, evidence validation, escalation of critical findings and comprehensive risk assessment reporting, enabling organizations to more effectively identify, document and act on third-party risk. The program also incorporates flexible support for M&A activity, audits and demand surges, helping health technology enterprises scale their third-party risk operations as business needs evolve.
“Organizations today need more than tools; they need operational execution that turns risk insights into action,” said Navin Balakrishnaraja, CEO and co-founder of Fortuna Cysec. “We are proud to partner with dynamic global health technology leaders to advance the maturity of their third-party risk programs through scalable, consistent processes that enhance visibility and strengthen governance across their vendor ecosystems. This underscores our commitment to helping regulated and enterprise organizations elevate cybersecurity, vendor risk and governance through hands-on execution, not just advisory support.”
About Fortuna Cysec
Fortuna Cysec is a global cybersecurity company offering Fortunox - an integrated AI-native Security Operations Platform that centralizes AI-powered threat detection, automated response, compliance management and true 24x7 managed detection and response. By combining advanced analytics, automated actions and expert-led response in one integrated system, Fortuna Cysec gives organizations a faster, smarter and more resilient way to defend their environments. For more information, visit www.fortunacysec.com.
Fortuna Cysec Delivers Scaled Third-Party Risk Management Services for Global Health Technology Sector
Fortuna Cysec, a global cybersecurity company offering integrated AI-native security operations managed detection and response, continuous threat exposure management and compliance services...